


By Levy Masiteng
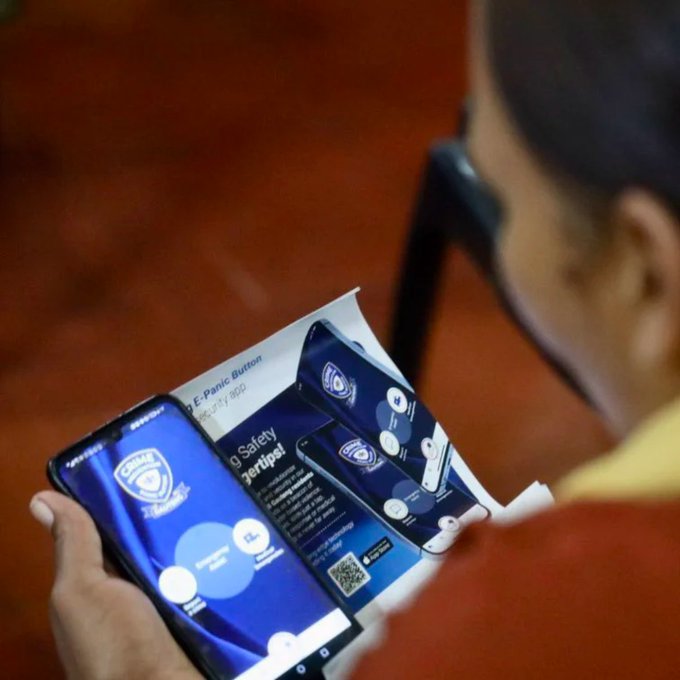
A security flaw in Gauteng’s e-Panic Button app may have exposed the personal details and locations of women reporting abuse.
The Gauteng Provincial Legislature’s Portfolio Committee on e-Government and Research and Development has now demanded urgent answers from the Department of e-Government over the breach.
In a media statement issued on Wednesday, committee chairperson Mbali Hlophe said the reported exposure raised serious concerns about the department’s responsibility to protect residents who rely on the app during emergencies.
The allegedly unsecured database contained the identities and locations of people who reported crimes, details of their complaints, photographs, contact information, vehicle registration numbers and, in some cases, identity numbers and medical aid information.
The problem was discovered by Stellenbosch University student Joel Cedras, with exposed location data allegedly dating back to the app’s launch in 2024.
ALSO READ: South Africa’s AI challenge is now implementation, says TUT
The committee said the exposed information included GPS coordinates and location histories that could reveal where users lived, worked or sought safety, while login codes were also reportedly exposed, potentially allowing someone with a registered user’s cellphone number to access the account.
“This is a failure that could cost lives,” Hlophe said.
The controversy comes amid ongoing investigations into a string of killings of women in Ekurhuleni since July, with police investigating whether some of the cases are connected.
The committee said the exposure of sensitive information could undermine public confidence in the app, particularly among women who depend on government services for protection against violence.
“The security of our systems and the protection of residents’ personal information are non-negotiable. The vulnerability was identified, and our technical teams implemented corrective measures promptly,” MEC for e-Government Bonginkosi Dhlamini said.
ALSO READ: KZN’s capital ‘falling apart’ as winds of change loom large
The department has said that no residents’ personal information was compromised.
But Hlophe said that claim must be supported by evidence, including independently examined access logs.
“The committee will not accept assurances without evidence,” Hlophe said.
She said the committee would investigate whether the department had fulfilled its legal obligations and whether previous assurances about the app’s security were accurate.
She said the committee would convene an urgent meeting with the department to establish when the “vulnerability” emerged, when officials became aware of it and what steps were taken to secure the database.
The committee has also demanded confirmation of whether the exposed information was accessed or misused, whether the Information Regulator was notified, and whether affected residents were informed.
Hlophe said the Protection of Personal Information Act (POPIA) requires the department to secure personal information, ensure its service providers do the same and notify the Information Regulator and affected residents following a security compromise.
Particular attention has been placed on protecting GBV survivors whose information may have been exposed.
ALSO READ: Sibiya regularly visited ‘the Farm’ and reported to Big Five cartel leader Msibi, says Sibanyoni
Hlophe said the department must explain what measures it is taking, together with police and support organisations, to identify and protect residents who reported gender-based violence through the app.
She added that the committee wanted the names of officials responsible for the app’s information security and the management of the platform contract, as well as confirmation of whether disciplinary processes had been initiated.
She said the committee was also seeking details of any action taken against the service provider, including breach notices, penalties, the recovery of public funds and whether termination of the contract or a ban from future government work was being considered.
The reported R269-million platform contract is under scrutiny, with the committee demanding the actual clauses governing data protection, cybersecurity, incident reporting, liability and POPIA compliance.
The department has been given seven days to submit a detailed written report, including security audits conducted and measures implemented to prevent a recurrence.
“Where negligence is established, officials and the service provider alike must face consequences. A contract worth hundreds of millions of rands cannot come with zero accountability when it fails the people it was meant to protect,” Hlophe said.